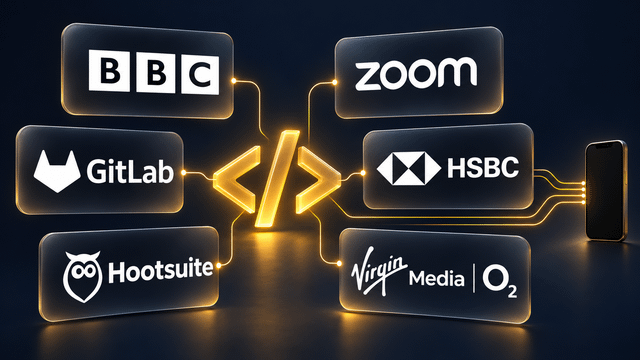
Heads up everyone. A massive supply-chain attack just hit several major third-party script providers (Optimizely,Kissmetrics, etc.), meaning legit sites like BBC, Zoom, CNN, and Salesforce have been unknowingly serving malicious JavaScript to their visitors.
While a lot of the mainstream infosec focus is on the fact that this drops an iPhone exploit loader, the payload includes built-in cryptocurrency wallet hijacking.
How the crypto theft works:
Address Replacement: The malicious script scans the pages you visit (and your clipboard) for crypto addresses. It validates the checksums and seamlessly swaps them out for the attacker’s addresses.
Wide Net: It has hardcoded replacement destinations for Ethereum/EVM, Bitcoin, TRON, TON, Solana, Litecoin,Bitcoin Cash, and Dogecoin.
Card Skimming: It’s also skimming payment card data from accessible forms.
Built-in Fallback: On some sites (like BBC), the payload is fully embedded. Even if your adblocker or DNS blocks the attacker’s external domain, the crypto-swapping script still executes locally.
The takeaway: Double-check every single address before you hit send, even if you are just browsing regular mainstream websites while making a transaction.
submitted by /u/Malwarebeasts [link] [comments]
r/CryptoCurrencyRead More
You might also be interested in reading Preserving and reinventing music festival legacy in the metaverse.