most explanations of the coldcard hack from back in july went straight into jargon — i needed a version that could stand up to the layman, while using it as a wedge for the tremendous responsibility that comes with self-custodying your assets. so… here goes:
the 12 or 24 english words that is your secret recovery seed phrase represents one enormous random number. every key and address in your wallet is calculated from that number, so whoever has the number has the money. that number is supposed to be drawn from a pool so big nobody could search it (analogously, the volume of the earth)
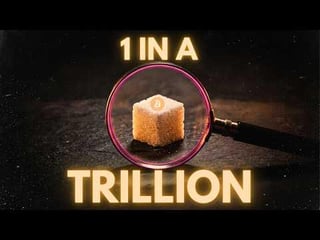
but a bug in the coldcard code allowed the “drawing” of this random number to come out of a much smaller pool between 2021 to 2026 (analogously, the volume of a sugar cube). attackers brute-forced through the smaller pool and emptied the matching wallets… approx. 1,200 of them in the first 41 minutes.
final damage: galaxy research puts total losses around $115M-130M.
but the words looked as if they were truly random. there was no way to tell by looking. which leaves an important question: if “don’t trust, verify” is such a core tenet to self-custody… what were we actually verifying as users?
one more evergreen point to be made… the wallets that held strong had at least one of these:
a strong passphrase (a “25th word” that came from the user themselves) 50+ fair, private dice rolls mixed into the seed multisig with private keys from different vendors and devices funds spread across seeds from more than one brandhave y’all implemented any of these?
i did a longer video breaking this down: https://youtu.be/ZCH_wCDzo3U
submitted by /u/haochizzle [link] [comments]
r/CryptoCurrencyRead More
You might also be interested in reading Trump Jr-linked media company projects $100M Dogecoin mining haul.